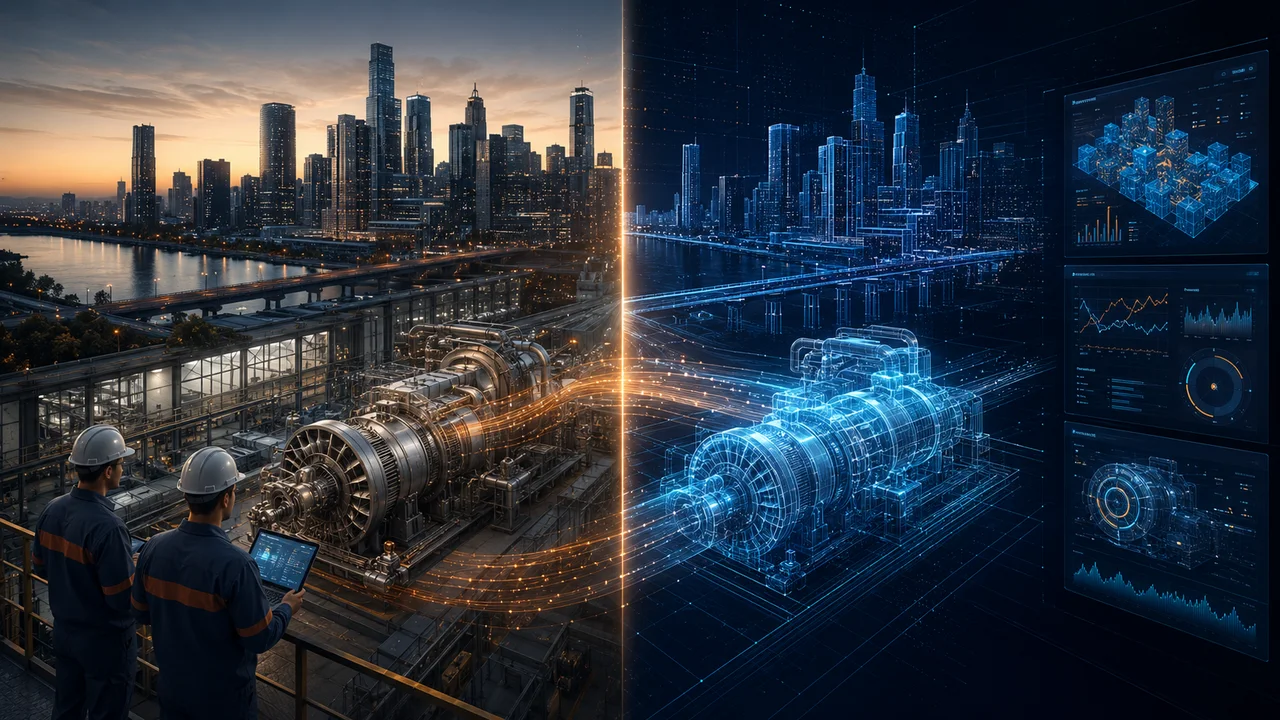
Digital twins connect models with real-world data to support planning and maintenance, but their value depends on accurate inputs and defined decisions. A digital twin connects a model of a physical asset or process with observations from the real world so people can monitor, test or plan decisions. The term covers systems of very different complexity. Value comes from a clearly defined decision and sufficiently accurate data, not from a visually impressive three-dimensional display. Models need maintenance as equipment and operating conditions change.
This guide develops digital twins through six specific lenses: models and sensors, asset monitoring, scenario testing, data quality, cybersecurity, and lifecycle ownership. The purpose is practical understanding. Readers should be able to recognise the mechanism, ask better questions of a provider or decision-maker and choose a proportionate next step without treating uncertainty as either proof of failure or permission for exaggerated claims.
The discussion considers the experience of users, administrators and product teams and keeps the analytical boundary wide enough to include connected services, device capability, data practices and human oversight. That matters because progress in digital twins should be visible through task completion, failure cases, security review, user control and support demand, not inferred from attention, purchase or participation alone.
Models and sensors in the context of Digital Twins Explained Through Real Uses
Models and sensors represent selected aspects of a machine, building, network or process. Sensors may measure temperature, vibration, position, flow or use, while the model encodes relationships relevant to a decision. No twin contains everything. Designers should state which features are represented, update frequency and where estimates replace direct measurement.
For digital twins, models and sensors should be evaluated as part of a connected system. It influences configuration, security, support and recovery, and those effects may appear at different times. Users, administrators and product teams need a shared description of the current situation before choosing an intervention. That description should cover connected services, device capability, data practices and human oversight; otherwise a successful first example may be treated as proof even though ordinary cases, exceptions or long-term responsibilities were never tested.
Set a decision threshold for models and sensors before investing further in digital twins. The threshold might concern quality, access, cost, reliability or harm, depending on the subject. Use task completion, failure cases, security review, user control and support demand and explain how long the observation must run. If the threshold is missed, decide whether the cause can reasonably be corrected. This protects the review from being rewritten after results appear simply to defend the preferred option.
The language used to describe models and sensors influences expectations. Marketing, policy or personal advice about digital twins should not turn a conditional benefit into a guaranteed outcome. State who the approach is intended for, what effort it requires and which limitations remain. Precise language helps suitable users make an informed choice and reduces disappointment that might otherwise be blamed on the people least able to influence the design.
Asset monitoring in the context of Digital Twins Explained Through Real Uses
Asset monitoring can identify abnormal conditions and help teams prioritise inspection. Alerts need thresholds that balance early warning with false alarms, plus a route for human review. A sensor fault can resemble an asset fault. Maintenance staff should see supporting evidence and record what they find so the model improves rather than becoming an unquestioned remote authority.
In this context, asset monitoring is not an isolated feature. It shapes decisions about configuration, security, support and recovery and influences the experience of users, administrators and product teams. A responsible assessment follows connected services, device capability, data practices and human oversight, including cases that do not use the preferred route. Those edge cases are useful design evidence. They reveal whether digital twins works because the system is dependable or only because the first participants had unusual resources and support.
Use a pre-mortem before changing asset monitoring. Imagine that the planned approach to digital twins has failed six months later and ask users, administrators and product teams to suggest plausible causes. Group those causes around configuration, security, support and recovery, then select signals from task completion, failure cases, security review, user control and support demand that could provide early warning. Assign a response to the most serious risks. This exercise is useful because people can discuss weakness without having to oppose the whole idea.
Equity also needs an explicit check. The average result for asset monitoring may hide a poor experience for beginners, smaller organisations, people with disabilities or communities with fewer resources. A sound discussion of digital twins compares outcomes across relevant groups and invites examples from the edges. The purpose is not to guarantee an identical experience in every circumstance, but to avoid calling a result successful while predictable barriers remain unexamined.
For a useful comparison with digital twins, read The Energy Footprint of Data Centres. Its subject is different, but it shows how neighbouring technology choices can expose dependencies that a narrow review misses.
Scenario testing in the context of Digital Twins Explained Through Real Uses
Scenario testing explores how an asset might respond to demand, weather, configuration or failure without disturbing the real system. Results depend on assumptions and validation against observed behaviour. Scenarios are especially useful for comparing options, not predicting one certain future. High-consequence decisions require uncertainty ranges and checks outside the modelling team.
A closer look at scenario testing changes what counts as progress in digital twins. Adoption or activity alone is weak evidence. Users, administrators and product teams should ask whether the intended outcome improved, whether the experience remained fair and whether the approach can be maintained. The analysis has to include connected services, device capability, data practices and human oversight. This is where hidden dependencies usually become visible and where a promising idea can be strengthened before it expands.
Test scenario testing with the smallest group that still represents the important variation in digital twins. Include a typical case, a difficult case and someone likely to need support. Gather task completion, failure cases, security review, user control and support demand, but also ask what participants expected and what surprised them. Correct avoidable confusion before interpreting the outcome. A pilot that teaches the procedure while measuring it may otherwise mistake unfamiliarity for a permanent limitation.
A resilience check asks what happens when normal resources are unavailable. For scenario testing in digital twins, consider loss of connectivity, staff absence, budget pressure, increased demand or a participant needing a different route. The response does not have to replicate ideal service perfectly, but it should protect the most important outcome. Testing recovery often reveals priorities more clearly than describing normal operation.
Data quality in the context of Digital Twins Explained Through Real Uses
Data quality includes accuracy, timing, coverage, calibration and context. Missing or misaligned data can produce a confident but misleading result. Establish ownership for sensors, interfaces and definitions, and monitor changes after software updates. More data is not automatically better; collect the minimum needed for the defined decisions and retain it only as long as justified.
Treating data quality seriously means connecting it with ownership. Someone must understand how it contributes to digital twins, what support is available and what would trigger a change of direction. Users, administrators and product teams should examine connected services, device capability, data practices and human oversight. The aim is not to remove every uncertainty before acting; it is to make the material uncertainties visible enough that a limited, reversible first step can be chosen.
To act on data quality, choose one real setting connected with digital twins and document the baseline. Ask users, administrators and product teams where friction, exclusion or misunderstanding currently occurs. Then test one bounded change and examine task completion, failure cases, security review, user control and support demand. Avoid changing several elements at once, because the team will not know which produced the result. Agree in advance on a stop condition as well as a success measure; stopping a weak idea is a valid use of a pilot.
Privacy, dignity and autonomy may be affected even when they are not the primary purpose of data quality. In digital twins, ask what information is collected, which choices remain available and whether refusing the preferred route creates a penalty. Proportionate safeguards should match the consequence. People need enough explanation to participate knowingly and a realistic way to correct a mistake or challenge an important outcome.
This aspect of digital twins also provides context for Robotics Beyond the Factory Floor. Reading the two articles together helps distinguish a general decision principle from the specific evidence required by each topic.
Cybersecurity in the context of Digital Twins Explained Through Real Uses
Cybersecurity matters because a connected model may reveal operations or influence controls. Separate monitoring from command where possible, authenticate devices and users, patch supported components and log important actions. Test recovery if connectivity or the platform fails. Access granted to vendors should be limited and removed when work ends.
Questions about cybersecurity involve both design and behaviour. A technically capable approach to digital twins may still fail if expectations, incentives or everyday routines work against it. Users, administrators and product teams should examine connected services, device capability, data practices and human oversight and identify the moment when people are most likely to abandon, misunderstand or work around the intended process. That moment is often a better starting point than adding another feature.
Implementation should remain proportionate to consequence. For a low-risk decision about cybersecurity, a short trial and simple notes may be sufficient; a high-consequence part of digital twins may require specialist review, formal approval and longer monitoring. In either case, collect task completion, failure cases, security review, user control and support demand. Make support and complaint routes clear before launch. People should not have to experience a serious failure before discovering who is responsible for correction.
Cost should be understood broadly. The price of cybersecurity within digital twins may include time, training, coordination, infrastructure and the burden of handling exceptions. A choice that looks inexpensive to one team may move unpaid work to customers, families or another public service. Record those transfers explicitly and compare them with the benefit before describing the approach as efficient.
Lifecycle ownership in the context of Digital Twins Explained Through Real Uses
Lifecycle ownership continues through design changes, repairs, new sensors and eventual retirement. A twin that is not updated may become less trustworthy than a simple current record. Budget for model validation, licences, data engineering and staff training. Preserve exportable documentation so the organisation can change provider or archive the twin with the physical asset.
Scale changes the meaning of lifecycle ownership. What works for a motivated first group may strain support, infrastructure or governance when digital twins reaches a wider audience. Users, administrators and product teams should model the effect on configuration, security, support and recovery and test connected services, device capability, data practices and human oversight under ordinary capacity, not only during a closely supported pilot. Expansion should be staged so evidence from one group can improve the experience of the next.
A useful workshop on lifecycle ownership would bring together users, administrators and product teams and map the experience from first contact through normal use, exception and recovery. Link each stage to digital twins and identify what information, skill or resource is required. Choose evidence from task completion, failure cases, security review, user control and support demand, but do not let measurement displace the outcome. A metric is worth keeping only when a change in it would lead to a specific decision.
One common mistake is to optimise the visible part of lifecycle ownership while ignoring maintenance and recovery. In digital twins, the long-term result depends on what happens after the first decision, when attention moves elsewhere and unusual cases appear. Document the smallest routine that keeps the improvement working. If that routine requires unavailable time, authority or skill, the design should be simplified before expansion rather than relying on permanent exceptional effort.
This aspect of digital twins also provides context for When Low-Code Tools Make Sense. Reading the two articles together helps distinguish a general decision principle from the specific evidence required by each topic.
Six questions to ask about digital twins
The following questions turn the six parts of digital twins into a focused review. They can be used by readers, teams or community groups without assuming that every setting needs the same answer.
- What does models and sensors mean in this setting, and who experiences its effects first?
- Which current problem involving asset monitoring is the article trying to solve?
- What evidence would show that scenario testing improved rather than merely changed?
- Who owns the long-term work associated with data quality, including exceptions?
- Which group could be poorly served by the preferred approach to cybersecurity?
- What result would justify revising or stopping work on lifecycle ownership?
Conclusion: a balanced view of Digital Twins Explained Through Real Uses
Digital Twins Explained Through Real Uses becomes useful when its six dimensions—models and sensors, asset monitoring, scenario testing, data quality, cybersecurity, lifecycle ownership—are understood together. The central promise is digital twins connect models with real-world data to support planning and maintenance, but their value depends on accurate inputs and defined decisions. That promise should remain connected to evidence, affected people and the resources required after the initial decision.
The next step is not automatic adoption or rejection. Choose one situation involving digital twins, document the current outcome and test a proportionate improvement. Review the result honestly, preserve what helped and change or stop what did not. That creates a stronger basis for configuration, security, support and recovery than confidence, novelty or fear alone.
Comments 0