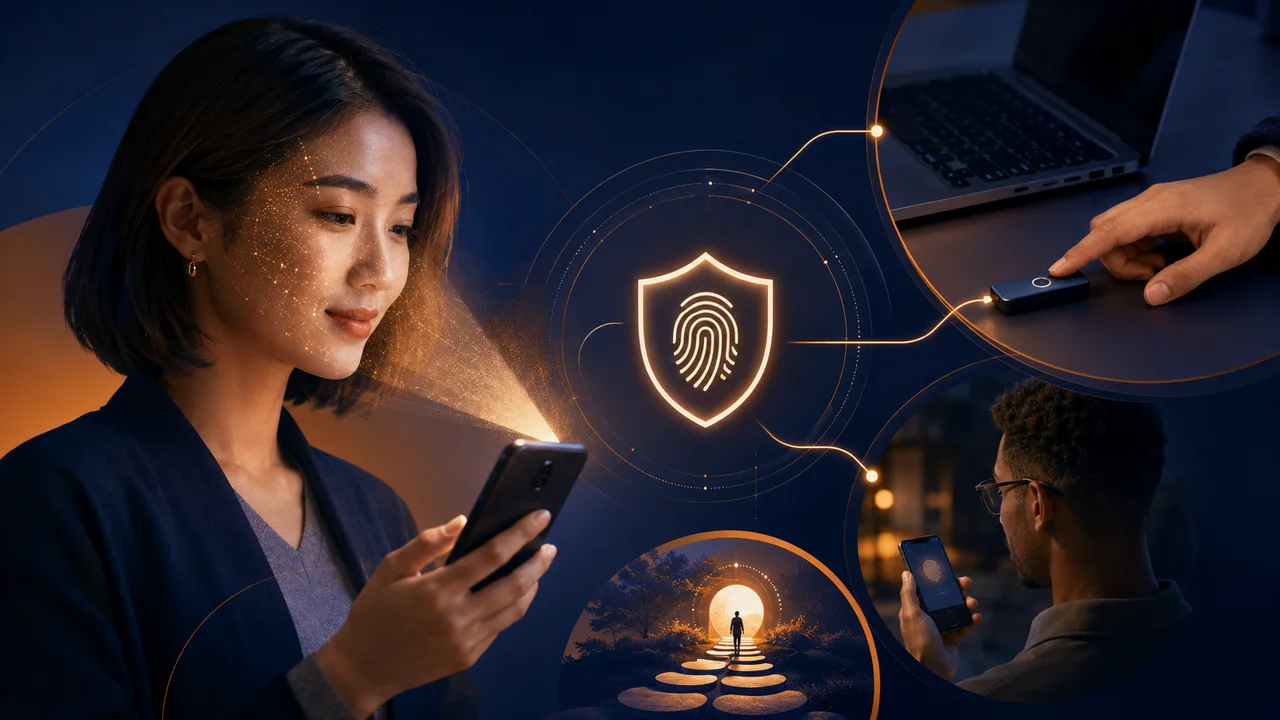
Passwordless sign-in can reduce stolen-password risk when organisations design enrolment, device loss and recovery with equal care. Passwordless authentication replaces a memorised shared secret with another way to prove control, commonly a cryptographic credential protected by a device unlock. Passkeys are a prominent example. The server stores a public key rather than a reusable password, while the private key remains protected on the user’s device or synchronised credential provider.
Passwordless Authentication Explained Simply is best understood by separating its main components and then reconnecting them. The sections below examine passkeys and devices, phishing resistance, user enrolment, lost-device recovery, shared-device access, and migration from passwords. These are not interchangeable labels: each describes a distinct decision, dependency or source of evidence. Together they show why the subject cannot be judged from one headline benefit or one alarming example.
The discussion considers the experience of users, administrators and product teams and keeps the analytical boundary wide enough to include connected services, device capability, data practices and human oversight. That matters because progress in passwordless authentication should be visible through task completion, failure cases, security review, user control and support demand, not inferred from attention, purchase or participation alone.
Passkeys and devices in the context of Passwordless Authentication Explained Simply
Passkeys and devices work through public-key cryptography. During registration, the device creates a key pair for the service. At sign-in, it proves possession of the private key after local verification such as a PIN or biometric. The biometric template normally unlocks the credential locally; it is not sent to every website as a replacement password.
A useful account of passkeys and devices should state both the direct effect and the conditions required to produce it. In passwordless authentication, those conditions may sit with different members of users, administrators and product teams. Mapping connected services, device capability, data practices and human oversight reveals whether authority and responsibility are aligned. If one group is accountable for an outcome but cannot change the factors driving it, the implementation plan needs redesign rather than stronger motivational language.
Test passkeys and devices with the smallest group that still represents the important variation in passwordless authentication. Include a typical case, a difficult case and someone likely to need support. Gather task completion, failure cases, security review, user control and support demand, but also ask what participants expected and what surprised them. Correct avoidable confusion before interpreting the outcome. A pilot that teaches the procedure while measuring it may otherwise mistake unfamiliarity for a permanent limitation.
Cost should be understood broadly. The price of passkeys and devices within passwordless authentication may include time, training, coordination, infrastructure and the burden of handling exceptions. A choice that looks inexpensive to one team may move unpaid work to customers, families or another public service. Record those transfers explicitly and compare them with the benefit before describing the approach as efficient.
Phishing resistance in the context of Passwordless Authentication Explained Simply
Phishing resistance comes from binding the credential to the legitimate site or application. A convincing imitation at a different domain cannot obtain a valid signature for the real service. This removes the common act of typing a password into a fraudulent page. It does not prevent every scam, account-recovery attack or malicious action after a legitimate session begins.
Scale changes the meaning of phishing resistance. What works for a motivated first group may strain support, infrastructure or governance when passwordless authentication reaches a wider audience. Users, administrators and product teams should model the effect on configuration, security, support and recovery and test connected services, device capability, data practices and human oversight under ordinary capacity, not only during a closely supported pilot. Expansion should be staged so evidence from one group can improve the experience of the next.
Before expanding work on phishing resistance, write a one-page implementation note for passwordless authentication. Include purpose, affected groups, owner, baseline, expected benefit, main risk and review date. Use task completion, failure cases, security review, user control and support demand to test the claim. Share the findings with the people affected, including an explanation of limitations. Clear reporting allows a result to be used in another setting without pretending that different resources or conditions will produce an identical outcome.
Timing can change the conclusion. A short observation of phishing resistance may capture novelty or setup problems rather than the durable effect on passwordless authentication. Choose a review period that reflects how the outcome develops and note seasonal or one-off influences. At the same time, define early warning signals that justify immediate action; waiting for a scheduled review is not responsible when evidence suggests preventable harm.
Within passwordless authentication, the decisions here connect naturally with Privacy-First Smartphones: What Users Should Know, which explores another part of technology where evidence, implementation and long-term responsibility must be considered together.
User enrolment in the context of Passwordless Authentication Explained Simply
User enrolment should explain which devices hold or can access the credential and how synchronisation works. Organisations may offer a passkey alongside existing methods during transition. Registration should require an already trusted session or strong verification, because an attacker who can add their own passkey has created a durable route back into the account.
The important shift is from recognising user enrolment as a desirable phrase to defining how it changes a real decision about passwordless authentication. Users, administrators and product teams may see different consequences, so the decision record should state whose experience is being used and whose may still be missing. The boundary for analysis is connected services, device capability, data practices and human oversight. Keeping that boundary visible prevents an attractive improvement in one place from transferring cost, risk or effort somewhere less visible.
To act on user enrolment, choose one real setting connected with passwordless authentication and document the baseline. Ask users, administrators and product teams where friction, exclusion or misunderstanding currently occurs. Then test one bounded change and examine task completion, failure cases, security review, user control and support demand. Avoid changing several elements at once, because the team will not know which produced the result. Agree in advance on a stop condition as well as a success measure; stopping a weak idea is a valid use of a pilot.
Interdependence deserves attention. Changes to user enrolment may rely on another team, public service, supplier or household behaviour outside the formal scope of passwordless authentication. List those dependencies and confirm which are merely assumed. A plan is fragile when every element must perform perfectly. Build a fallback for the dependency most likely to fail and practise the handover before pressure makes improvisation necessary.
Lost-device recovery in the context of Passwordless Authentication Explained Simply
Lost-device recovery must be designed before passwords are removed. Synced passkeys may become available on another authenticated device; hardware security keys can provide a separate backup; and recovery codes can be stored offline. Support agents need clear checks for high-risk recovery. A convenient fallback that uses only weak personal information can undo the security advantage.
Different participants may use the phrase lost-device recovery while referring to different problems. In a discussion of passwordless authentication, users, administrators and product teams should define the term with a concrete example and relate it to configuration, security, support and recovery. This avoids false agreement. It also makes it possible to inspect connected services, device capability, data practices and human oversight and decide whether the proposed action addresses the original need or merely changes the most visible symptom.
Set a decision threshold for lost-device recovery before investing further in passwordless authentication. The threshold might concern quality, access, cost, reliability or harm, depending on the subject. Use task completion, failure cases, security review, user control and support demand and explain how long the observation must run. If the threshold is missed, decide whether the cause can reasonably be corrected. This protects the review from being rewritten after results appear simply to defend the preferred option.
Communication should distinguish established evidence, reasonable expectation and speculation. Claims about lost-device recovery in passwordless authentication become more trustworthy when readers can see the setting, timeframe and limitation behind them. Plain language does not require pretending the issue is simple. It requires defining specialised terms, explaining the consequence of uncertainty and showing which decision can responsibly be made with the information available now.
For a useful comparison with passwordless authentication, read Cloud Computing for Small Organisations. Its subject is different, but it shows how neighbouring technology choices can expose dependencies that a narrow review misses.
Shared-device access in the context of Passwordless Authentication Explained Simply
Shared-device access needs special handling in schools, libraries, families and frontline workplaces. Users should not leave personal credentials available to the next person. Cross-device sign-in, roaming security keys or managed profiles may be more suitable than saving a passkey locally. Sign-out and profile separation must be understandable, especially where digital confidence varies.
For passwordless authentication, shared-device access should be evaluated as part of a connected system. It influences configuration, security, support and recovery, and those effects may appear at different times. Users, administrators and product teams need a shared description of the current situation before choosing an intervention. That description should cover connected services, device capability, data practices and human oversight; otherwise a successful first example may be treated as proof even though ordinary cases, exceptions or long-term responsibilities were never tested.
A practical review can begin with three columns: the current position on shared-device access, the change being considered and the evidence that would justify keeping it. For passwordless authentication, suitable evidence includes task completion, failure cases, security review, user control and support demand. Select a small number of measures before the result is known, add direct observations and record exceptions. Set a review date and name the person able to correct the design. If the evidence is mixed, retain the useful element while narrowing or revising the weak one.
One common mistake is to optimise the visible part of shared-device access while ignoring maintenance and recovery. In passwordless authentication, the long-term result depends on what happens after the first decision, when attention moves elsewhere and unusual cases appear. Document the smallest routine that keeps the improvement working. If that routine requires unavailable time, authority or skill, the design should be simplified before expansion rather than relying on permanent exceptional effort.
Migration from passwords in the context of Passwordless Authentication Explained Simply
Migration from passwords should be gradual and measurable. Begin with willing users and important accounts, monitor failed registration and recovery, then improve instructions before broader rollout. Keep legacy routes protected during the transition because attackers will target the weakest remaining method. Success includes fewer takeovers and support problems, not only the number of passkeys created.
The consequences of migration from passwords may appear before, during and long after the main decision about passwordless authentication. That timing matters to users, administrators and product teams, because an early convenience can be followed by maintenance, support or access problems. Review connected services, device capability, data practices and human oversight at each stage and identify who has authority to respond. A benefit that depends on unresolved work being absorbed elsewhere should not be described as a complete improvement.
A useful workshop on migration from passwords would bring together users, administrators and product teams and map the experience from first contact through normal use, exception and recovery. Link each stage to passwordless authentication and identify what information, skill or resource is required. Choose evidence from task completion, failure cases, security review, user control and support demand, but do not let measurement displace the outcome. A metric is worth keeping only when a change in it would lead to a specific decision.
Responsibility should continue after launch. Decisions about migration from passwords in passwordless authentication need an owner who can answer questions, maintain the approach and respond when conditions change. Name a backup and keep essential information where the relevant people can find it. When responsibility exists only during a project meeting, predictable problems become urgent surprises and the people affected are left to discover their own workaround.
Within passwordless authentication, the decisions here connect naturally with Quantum Computing: Promise Versus Reality, which explores another part of technology where evidence, implementation and long-term responsibility must be considered together.
Six questions to ask about passwordless authentication
The following questions turn the six parts of passwordless authentication into a focused review. They can be used by readers, teams or community groups without assuming that every setting needs the same answer.
- What does passkeys and devices mean in this setting, and who experiences its effects first?
- Which current problem involving phishing resistance is the article trying to solve?
- What evidence would show that user enrolment improved rather than merely changed?
- Who owns the long-term work associated with lost-device recovery, including exceptions?
- Which group could be poorly served by the preferred approach to shared-device access?
- What result would justify revising or stopping work on migration from passwords?
Conclusion: a balanced view of Passwordless Authentication Explained Simply
Passwordless Authentication Explained Simply becomes useful when its six dimensions—passkeys and devices, phishing resistance, user enrolment, lost-device recovery, shared-device access, migration from passwords—are understood together. The central promise is passwordless sign-in can reduce stolen-password risk when organisations design enrolment, device loss and recovery with equal care. That promise should remain connected to evidence, affected people and the resources required after the initial decision.
The next step is not automatic adoption or rejection. Choose one situation involving passwordless authentication, document the current outcome and test a proportionate improvement. Review the result honestly, preserve what helped and change or stop what did not. That creates a stronger basis for configuration, security, support and recovery than confidence, novelty or fear alone.
Comments 0